IPsec VPN Between Cisco ASA and HPE MSR935 (Comware v5)
Full configuration example for a site-to-site IKEv1 IPsec VPN between a Cisco ASA and an HP MSR935 running Comware v5, including a fix for one-way traffic.
Legacy platform.
Comware v5 is end-of-sale on most platforms. This guide is kept for anyone still running it; check syntax against your software release, and see the Comware v7 guides for current platforms.
Full site-to-site IKEv1 IPsec VPN configuration between a Cisco ASA and an HP MSR935 (Comware v5).
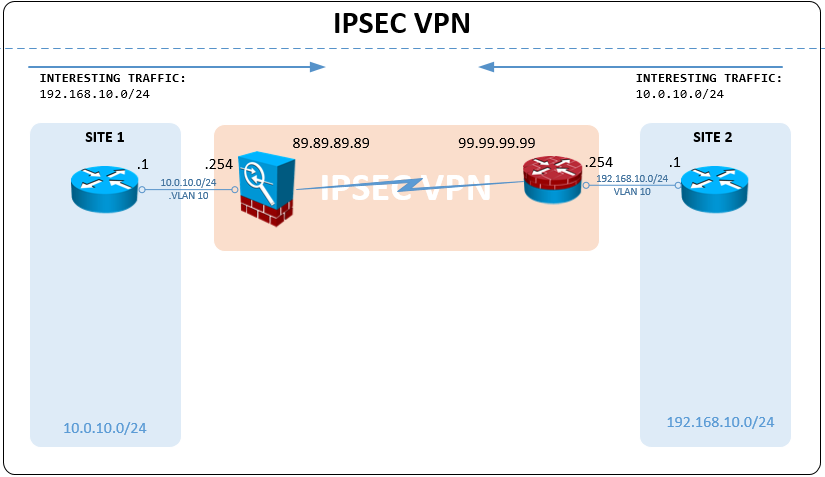
Tested versions: Cisco ASA 9.1(2), HP MSR935 Comware 5.20.106 Release 2513P09
Addressing: ASA WAN 89.89.89.89, MSR WAN 99.99.99.99, ASA LAN 10.0.0.0/24, MSR LAN 192.168.10.0/24
Phase 1 — IKE #
ASA:
crypto ikev1 policy 5
 authentication pre-share
 encryption aes-192
 hash sha
 group 2
 lifetime 3600

group-policy GroupPolicy_99.99.99.99 internal
group-policy GroupPolicy_99.99.99.99 attributes
 vpn-tunnel-protocol ikev1

tunnel-group 99.99.99.99 type ipsec-l2l
tunnel-group 99.99.99.99 general-attributes
 default-group-policy GroupPolicy_99.99.99.99
tunnel-group 99.99.99.99 ipsec-attributes
 ikev1 pre-shared-key YOUR-PSK-HERE
MSR935:
ike proposal 2
 encryption-algorithm aes-cbc 192
 dh group2
 sa duration 3600

ike peer VPN-SITE1-TO-SITE2
 proposal 2
 pre-shared-key YOUR-PSK-HERE
 remote-address 89.89.89.89
 local-address 99.99.99.99
 nat traversal
Phase 2 — IPsec #
ASA:
crypto map outside_map 1 match address outside_cryptomap
crypto map outside_map 1 set peer 99.99.99.99
crypto map outside_map 1 set ikev1 transform-set ESP-AES-192-SHA
crypto map outside_map 1 set security-association lifetime seconds 28800
crypto map outside_map 1 set security-association lifetime kilobytes 1843200
crypto map outside_map interface outside
MSR935:
ipsec transform-set vpn.1
 encapsulation-mode tunnel
 transform esp
 esp authentication-algorithm sha1
 esp encryption-algorithm aes-cbc-192

ipsec policy vpn 1 isakmp
 connection-name vpn.1
 security acl 3001
 pfs dh-group2
 ike-peer VPN-SITE1-TO-SITE2
 transform-set vpn.1
 sa duration traffic-based 1843200
 sa duration time-based 28800
Interesting traffic ACLs #
ASA:
object network SITE-1
 subnet 10.0.0.0 255.255.255.0
object network SITE-2
 subnet 192.168.10.0 255.255.255.0
access-list outside_cryptomap extended permit ip object SITE-1 object SITE-2
MSR935:
acl number 3001
 rule 5 permit ip source 10.0.10.0 0.0.0.255 destination 192.168.10.0 0.0.0.255
 rule 10 permit ip source 192.168.10.0 0.0.0.255 destination 10.0.10.0 0.0.0.255
Fix: one-way traffic after tunnel comes up #
The tunnel builds but you see encaps on the ASA with no decaps. This is a routing issue on the MSR. Add a static route on the MSR pointing the remote LAN via the ASA WAN IP:
ip route-static 10.0.0.0 255.255.255.0 89.89.89.89Traffic flows bi-directionally after adding this.